Meta fixes Muse zero-day vulnerability, raises security visibility concerns
Meta's Muse Mac app had a zero-day vulnerability that allowed malware to hijack authentication credentials without special permissions, effectively turning it into a backdoor. Despite a quick patch, …
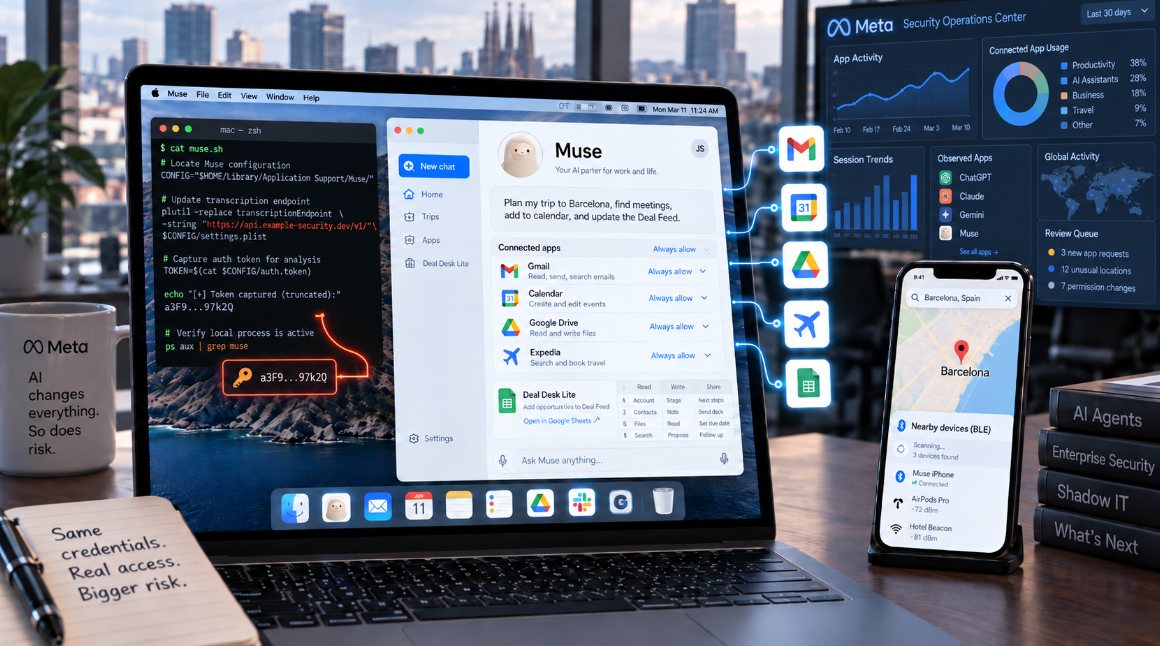
Patrick Wardle, founder of the Objective‑See Foundation and a former NASA and NSA employee, disclosed a zero‑day vulnerability in Meta’s Muse Mac app on Monday, showing that malware already running under a standard macOS user account could hijack the agent’s authentication material without needing any special system permissions. The flaw let an attacker seize the credentials that Muse uses to communicate with Meta’s security services, effectively turning the legitimate app into a backdoor.
The discovery comes as Muse, Meta’s endpoint‑security agent for macOS, has seen rapid adoption, reaching more than 2.5 million downloads in its first 13 days according to analytics firm Sensor Tower. The app is marketed to businesses and individuals as a way to protect devices from phishing, ransomware and other threats, and its swift uptake reflects growing demand for cloud‑based security solutions on Apple computers. The timing of the disclosure highlights how quickly new security tools can become widespread targets for exploitation, especially when they handle sensitive authentication tokens.
Wardle demonstrated the impact of the flaw by compromising a Muse session and extracting the location of a linked iPhone, which he traced to Barcelona. He then triggered a Bluetooth Low Energy scan from the compromised Mac, showing that the attacker could extend control to nearby devices. The episode underscores a broader problem: security teams often lack visibility into what privileged agents like Muse can access or do once installed, making it difficult to detect malicious misuse of legitimate software.
Meta issued a patch for the vulnerability within hours of the public disclosure, but experts warn that the fix alone does not solve the underlying visibility gap. Organizations are urged to audit the permissions granted to security agents, monitor their network activity, and consider additional controls such as zero‑trust policies. As more firms rely on third‑party security software, the incident serves as a reminder that even trusted tools can become attack vectors if their inner workings remain opaque.
Read Full Story at VentureBeat →